
Mithun Sanghavi — Global Cybersecurity & Risk Transformation Leader

Mumbai, India · CISO / vCISO
25+ years architecting enterprise cyber resilience, security governance, and risk transformation across BFSI, manufacturing, insurance, and global consulting ecosystems.
0+
Years of Experience
$0+M
Total Cybersecurity Portfolio Managed
0+
Team Members Led Till Date
0+
Industry Awards
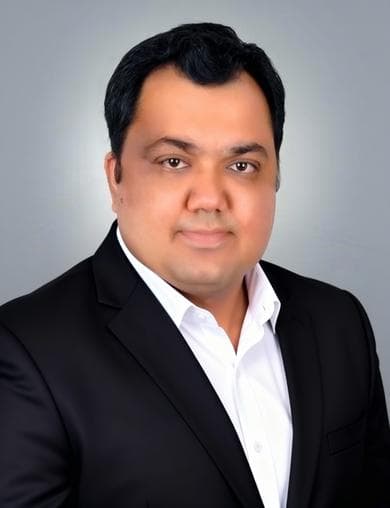
About
Enterprise cybersecurity strategist, board advisor
Enterprise Cybersecurity Strategist and Transformation Leader with 25+ years of experience architecting enterprise-wide cyber resilience, security governance, risk transformation, and regulatory compliance strategies across BFSI, NBFC, Oil & Gas, Healthcare, Technology, Telecommunications, E-commerce, Education, and Aviation, within global enterprise and consulting ecosystems spanning the US, EMEA, APAC, and ANZ regions.
Trusted Board- and CXO-level Cybersecurity Advisor with expertise in translating complex cyber threat landscapes, emerging risks, and regulatory requirements into actionable security strategies and business-aligned roadmaps. Extensive experience leading SOC transformation, incident response, cyber resilience programs, vulnerability management, Data Loss Prevention (DLP), identity security, cloud security, enterprise security architecture, and IT Governance, Risk & Compliance (GRC), aligned with regulatory and industry frameworks including India's Digital Personal Data Protection Act, 2023 (DPDP Act), GDPR, NIST CSF, ISO 27001, NIS2, RBI cybersecurity guidelines, and ITAR.
Read full profile →Recognition
Awards & Accolades
Recent industry recognition for cybersecurity leadership, transformation, and AI security governance.
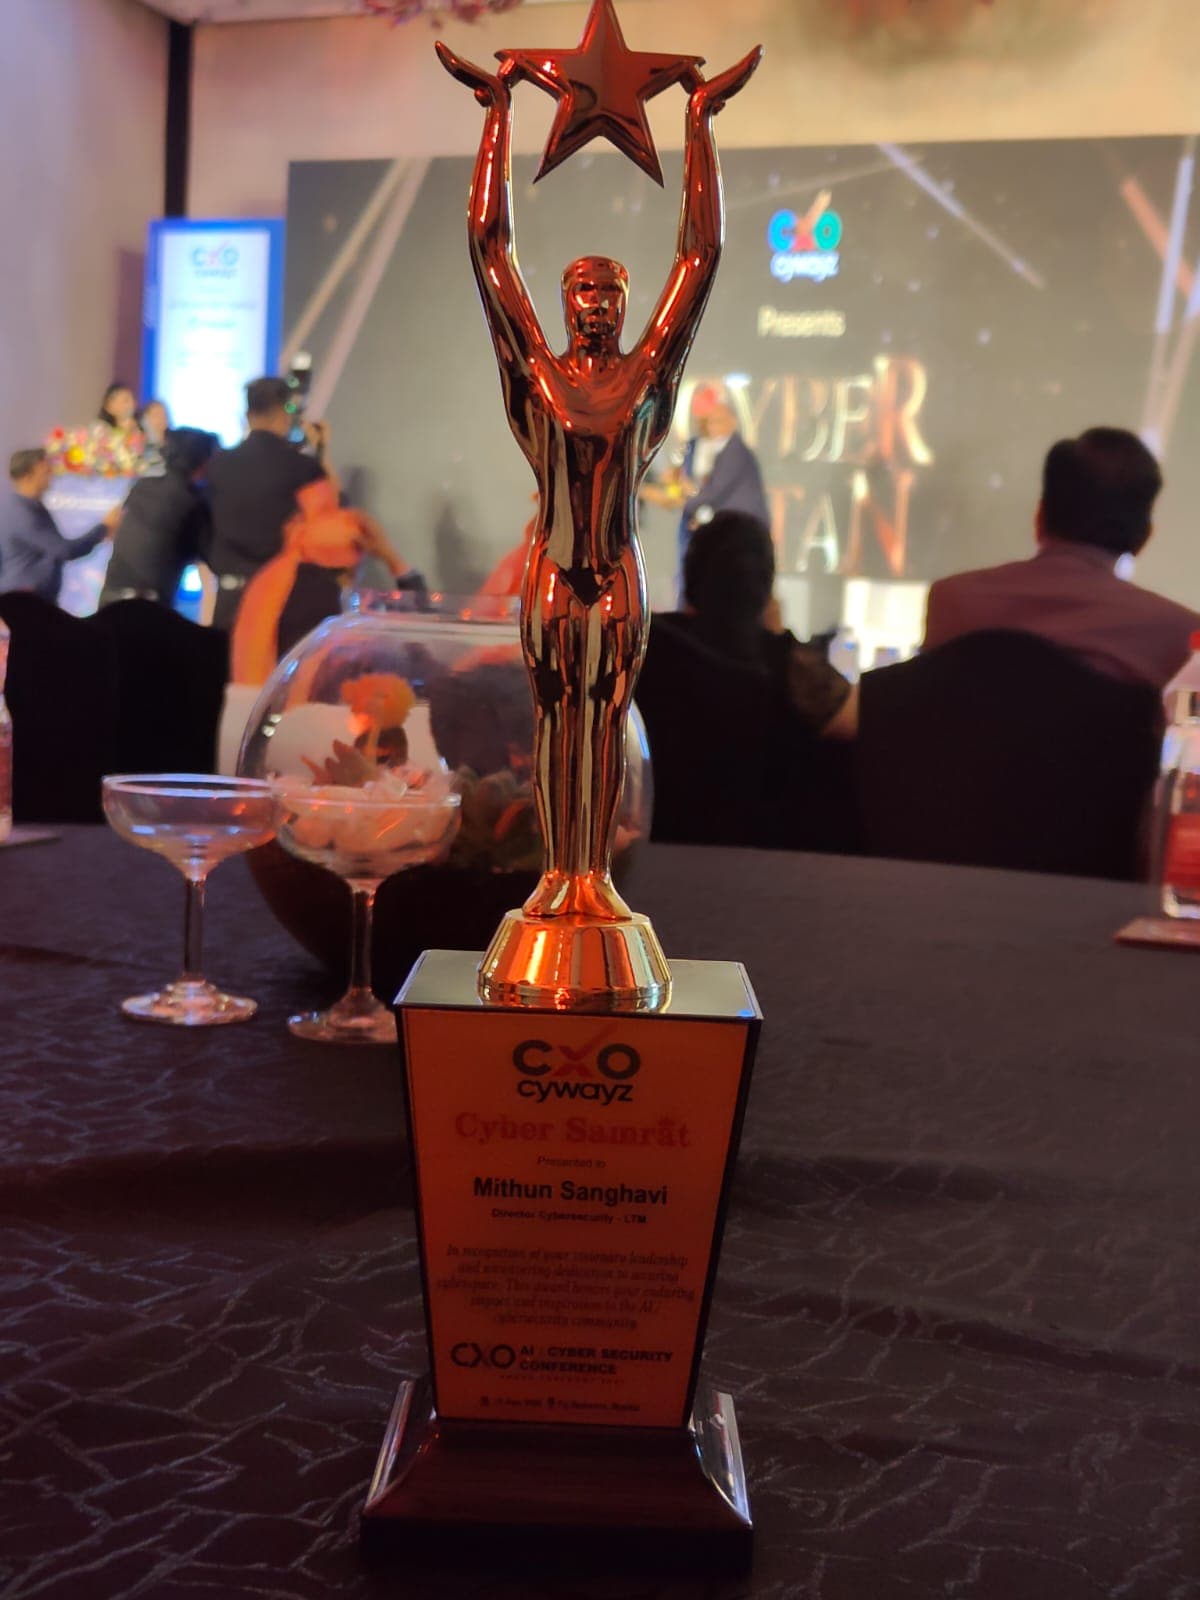
2026
Cyber Samrat Award
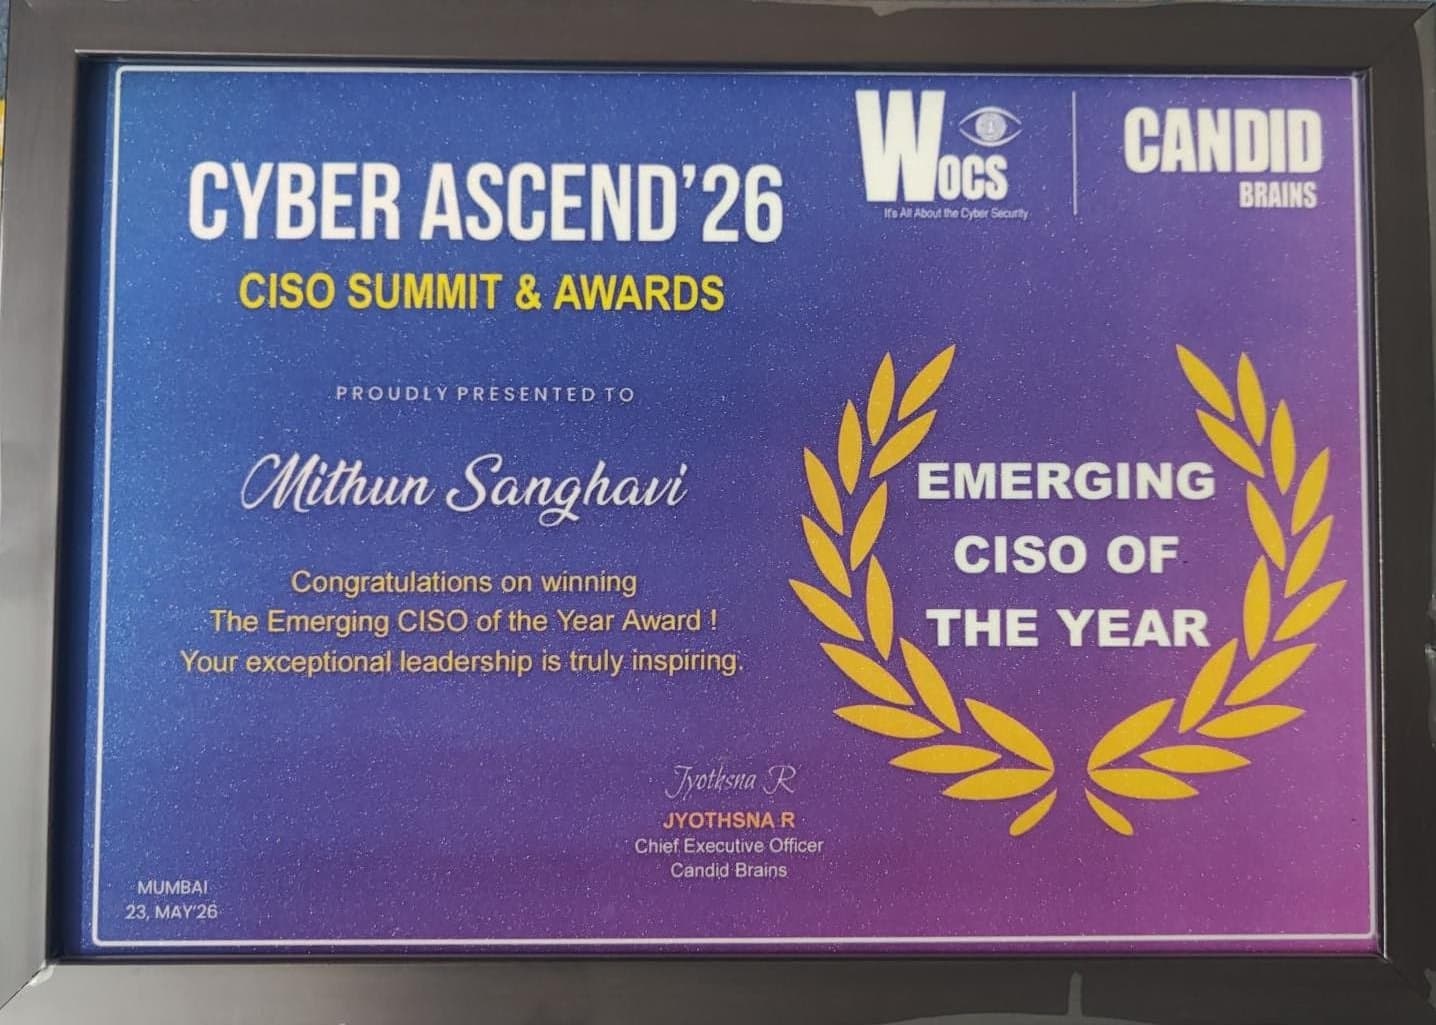
2026
Emerging CISO of the Year
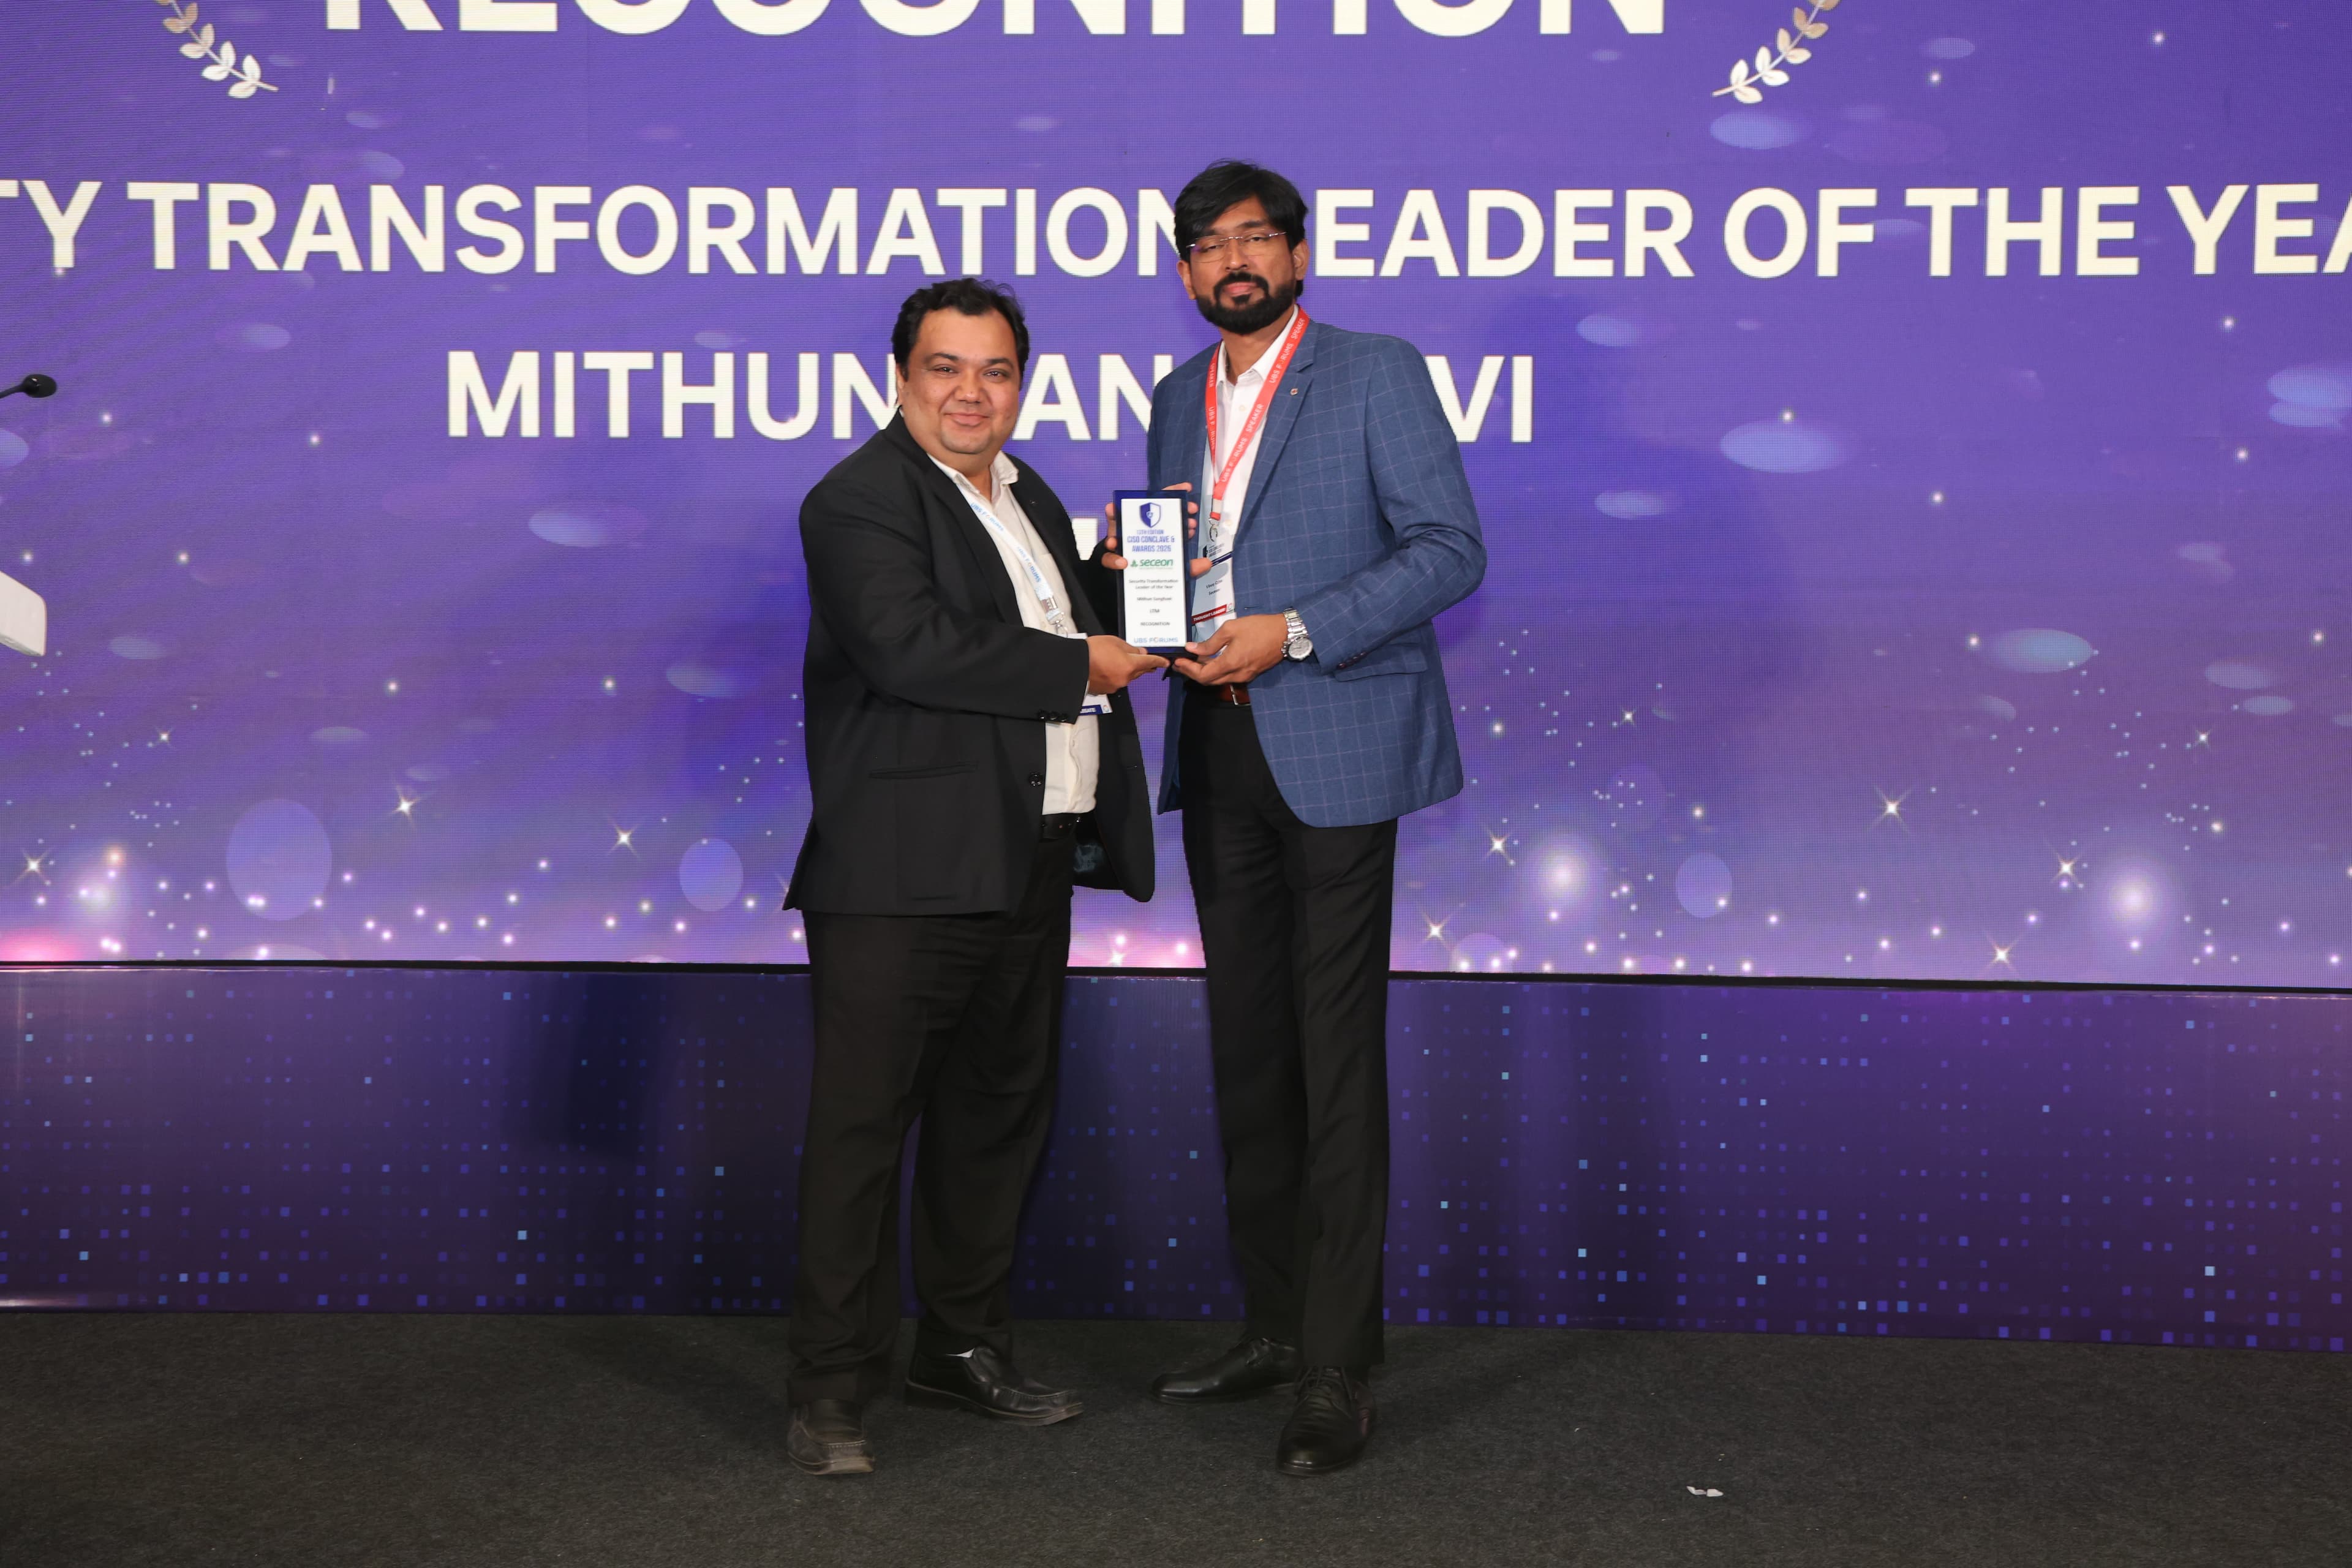
2026
Security Transformation Leader of the Year
Advisory
How I Help Organizations
From board-level vCISO advisory to hands-on SOC transformation, engagements are scoped around enterprise risk and business outcomes.
Virtual CISO (vCISO)
Board-level cybersecurity leadership on demand — strategy, risk appetite, security roadmaps, and executive reporting without the cost of a full-time CISO.
Cyber Risk & GRC Advisory
Governance, risk, and compliance programs mapped to DPDP Act 2023, GDPR, NIST CSF, ISO 27001, NIS 2.0, RBI, and ITAR — turned into actionable roadmaps.
Cyber Resilience & Incident Response
Crisis governance, business continuity, and incident response frameworks built to reduce MTTD/MTTR and protect critical business processes.
AI Security & AI Governance
AI-first security strategy, LLM/agentic AI risk assessment, and operationalizing AI controls for enterprises adopting AI at scale.
SOC & Threat Intelligence Transformation
Design and modernization of SOC, SIEM, EDR/XDR, and threat intelligence operations across cloud, IT/OT, and IoT environments.
Board & CXO Cybersecurity Briefings
Translating complex threat landscapes and regulatory mandates into clear, actionable briefings for Boards and executive leadership.
Let's Talk